News
CSA urges Universities to strengthen cybersecurity following university of Nottingham cyber-attack


The Cyber Security Authority (CSA) has cautioned universities and other operators of Critical Information Infrastructure (CII) in Ghana to comply with cybersecurity regulations following a recent cyber-attack on the University of Nottingham in the United Kingdom.
In a press release issued on June 16, 2026, the Authority said the incident should serve as a warning to educational institutions that no organisation is immune to cyber threats, regardless of its size, reputation or technological capacity.
According to the CSA, the attack on the University of Nottingham is believed to have affected about 450,000 students and alumni, exposing sensitive information such as personal records, contact details, student identification information and financial data.
The Authority noted that although the breach occurred outside Ghana, it has important lessons for the country’s education sector as well as other critical sectors including health, telecommunications and transportation.
The CSA explained that Ghanaian universities are increasingly relying on digital technologies such as student information systems, online learning platforms, cloud services, digital payment systems and research collaborations.
While these technologies improve efficiency and access to services, they also create opportunities for cybercriminals to exploit vulnerabilities.
“The question is therefore not whether Ghanaian universities or other critical sectors will be attacked, but whether they are sufficiently prepared when an attack occurs,” the statement said.
The Authority reminded institutions to adhere to the Directive for the Protection of Critical Information Infrastructure, which was launched in October 2021 to strengthen cybersecurity across critical sectors.
According to the CSA, the directive requires organisations to establish cybersecurity governance structures, conduct risk assessments, implement security controls, report incidents, carry out regular audits and develop effective incident response plans.
The Authority said these measures are intended to reduce the likelihood and impact of cyber-attacks and help protect essential services and national interests.
By: Jacob Aggrey

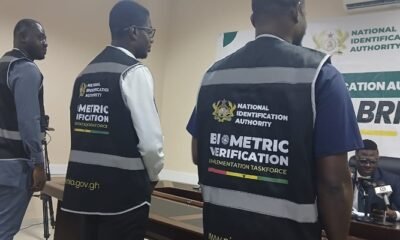




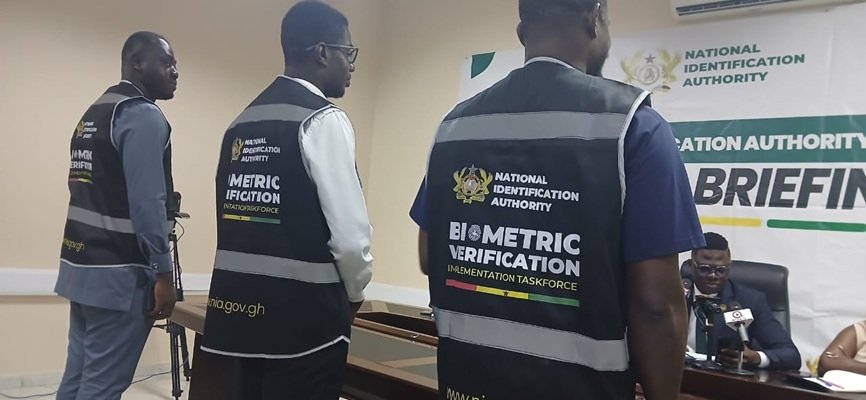
The National Identification Authority (NIA) has announced the commencement of enforcement of the National Identity Register (Amendment) Regulations, 2026 (L.I. 2523), warning institutions that fail to comply with the new requirements of possible fines of up to 2,000 penalty units.
The Authority says it will deploy a Biometric Verification Implementation Task Force to inspect institutions and ensure they comply with the regulations, following the expiration of a three-month grace period granted to businesses and public institutions.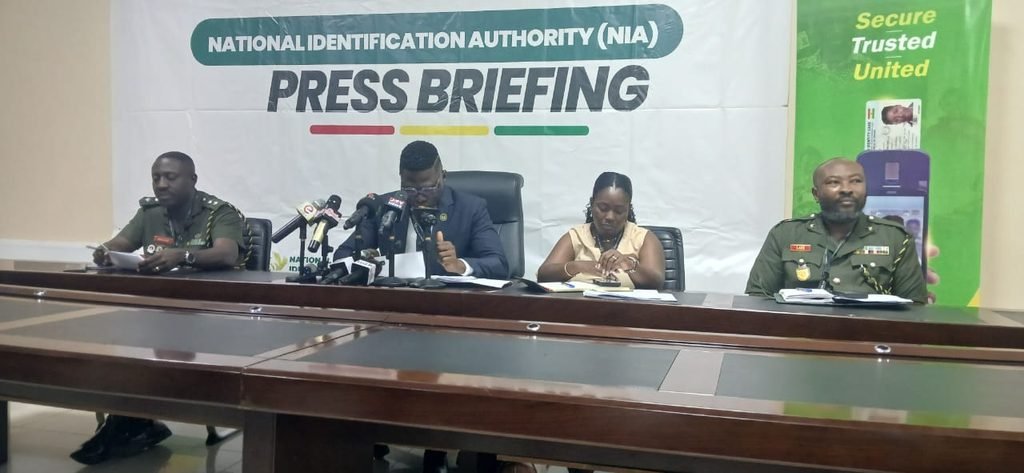
Speaking at a press briefing in Accra on Monday, November 2, 2026, the NIA’s Corporate Affairs representative, William Ampomah Emmanuel Darlas, said the Authority had completed its public education and stakeholder engagement activities and was now moving into the enforcement and compliance monitoring phase.
He explained that the regulations require institutions that verify the identities of customers or applicants as part of their operations to use the NIA’s approved biometric verification platform instead of relying solely on visual inspection of the Ghana Card.
Under the new rules, institutions are prohibited from photocopying, scanning or keeping copies of the Ghana Card for identity verification purposes.
Mr Darlas stressed that simply collecting a customer’s Ghana Card, looking at the photograph and comparing it with the person presenting it would no longer be accepted as a valid method of identity verification.
He, however, clarified that the Ghana Card remains the country’s official national identity document and that citizens are not required to register for a new card or capture their biometrics again under the new regulations.
He said the new system is intended to reduce identity fraud, impersonation and other crimes by ensuring that the person presenting the Ghana Card is the actual owner.
According to him, the biometric verification process will rely on information already captured during Ghana Card registration, including fingerprints, iris details and facial features stored in the card’s chip.
Mr Darlas warned institutions against using third-party companies or individuals to access the NIA’s identity verification platform, insisting that the Authority does not work with intermediaries.
He said institutions seeking access to the National Identity Register must deal directly with the NIA and complete its official onboarding process.
The process requires institutions to prove that they are legally registered companies in Ghana, obtain certification from the Data Protection Commission and work with the NIA’s technical team to establish the necessary connection to its platform.
He further cautioned institutions already connected to the platform against subletting their access to other businesses, particularly small and medium-sized enterprises.
He disclosed that the Authority had received reports of some institutions providing their verification services to other businesses without the NIA’s approval and warned that those involved would face legal action.
Mr Darlas said organisations that fail to comply with L.I. 2523 could face fines ranging from 500 to 2,000 penalty units, depending on the nature of the offence.
He explained that the NIA does not have the authority to impose the fines directly but would take offenders to court for the appropriate punishment.
He indicated that Institutions found guilty could also face additional administrative measures, including being barred from accessing the NIA’s verification platform in the future.
The NIA representative further clarified that the new regulations do not prohibit all institutions from physically using the Ghana Card during transactions.
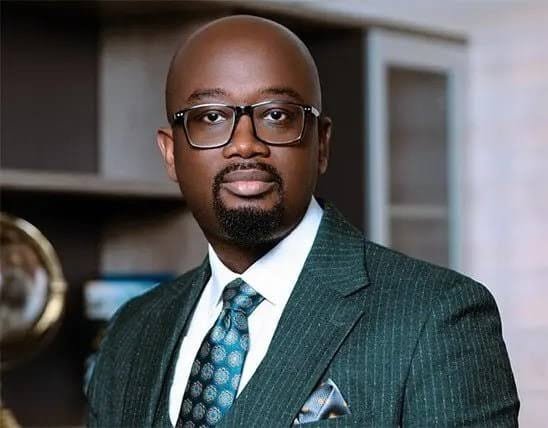
The Managing Director of the Ghana Publishing Company Limited, Nana Kwesi Boatey, has revealed how he transformed a major overstaffing challenge into a success story through the government’s 24-Hour Economy initiative.
Speaking at the Government Accountability Series on Monday, November 2, Mr. Boatey disclosed that when he assumed office in February 2025, and inherited a bloated workforce of 250 employees doing work that could be efficiently handled by 150 people, a situation that created serious liquidity challenges for the state-owned company.
Instead of resorting to downsizing, he adopted an innovative approach by instituting a 24-hour operational system.
Under the new system, staff were redistributed across three shifts: 7 a.m. – 4:30 p.m., 10 a.m. – 7 p.m., and 10 p.m. – 4:30 a.m.
This not only ensured optimal use of labour but also maximized machine utilization and improved overall output.
According to him, the single move redefined the productivity culture within the company, reinforcing discipline, accountability, and efficiency.
The Ghana Publishing Company’s turnaround is being cited as a practical example of how the 24-Hour Economy policy can drive growth without job losses.
By Edem Mensah-Tsotorme